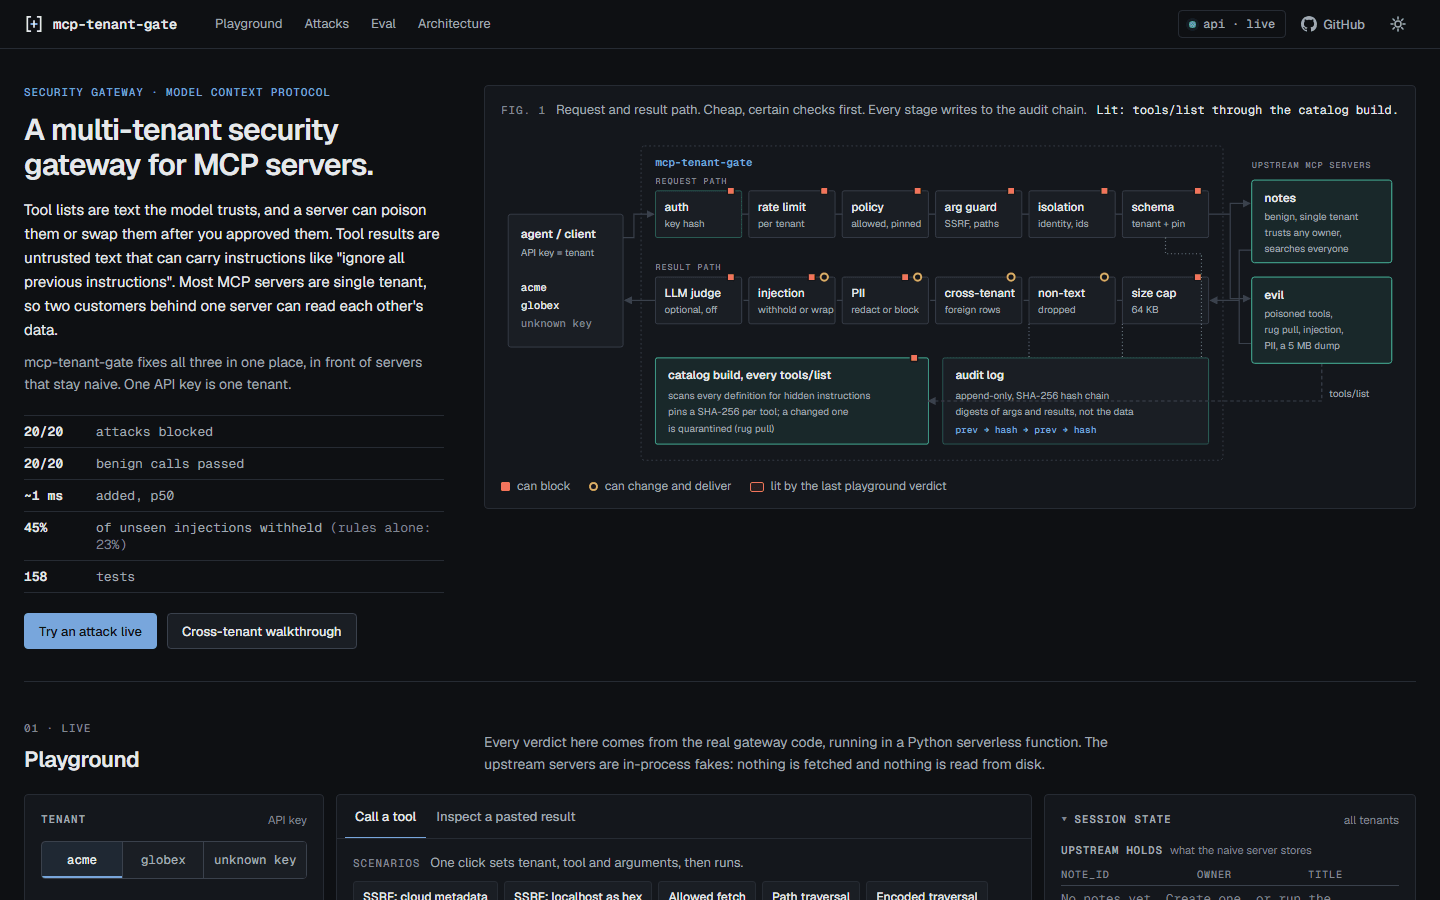
Teams wire AI agents to MCP servers they did not write. The tool list is an attack surface, tool results are untrusted text, and most servers are single-tenant. mcp-tenant-gate fixes these in one place, in front of servers that stay naive.
It isolates tenants, hides poisoned or shadowing tool definitions, blocks SSRF and path traversal arguments, redacts personal data and keeps a hash-chained audit log. It blocks 20 of 20 scripted attacks.
On a public prompt-injection dataset it had never seen, the rules alone withhold about 1 in 4 injections. I published that number and an error analysis of every miss, because a security tool that hides its limits is worse than none.
The live playground runs the real gateway code: switch tenants, try attacks, and see allow, redact or block with the reason.
Stack used
What I learned
- •Threat-modelling an agent protocol (MCP) and building defences layer by layer
- •Measuring a security control on held-out data and reporting the misses honestly
- •Shipping a Python serverless playground that runs real code safely